
Straight answers about how secure your business really is
We look at your business the way an attacker would, then give you a plan ranked by what matters most, and help you see it through until every item is closed.
Simple questions, hard to answer
Is our email set up properly? Could someone pretend to be us? What can an attacker see from the internet? Most business owners and finance directors cannot answer these with confidence, and the usual audit does not help much: it hands over a long list of findings and leaves. The list sits in a folder, and nothing changes until something goes wrong.
What it means for your business
Straight answers
Plain-language answers about where you are exposed, including after an incident, when you need to know what happened and whether it is over.
A plan you can act on
Every finding ranked critical, high or medium, with fixes balanced against how your people work.
Followed through to close
We stay with the plan until items are fixed, and show you the progress, rather than handing over a report and leaving.
No strings attached
Already have an IT provider? We share the findings with them so they can do the work.
What we assess
Choose the modules that fit your business. Each one is a fixed scope at a fixed price.
SiSmic Surface
What anyone on the internet can see: your domains, email security, exposed systems and lookalike domains.
SiSmic Endpoint
Your laptops, desktops and servers: missing updates, known vulnerabilities and risky configuration.
SiSmic Network
Your firewall, switches and Wi-Fi: vulnerability scanning and configuration review from the inside.
- Microsoft 365 security configuration, including Secure Score and email forwarding rules
- Log analysis to find activity that should not be there
- A ranked remediation plan and an executive summary for the board
- Optional monthly monitoring of your internet-facing systems
The free Security Risk Assessment is a lighter version of SiSmic Surface.
What you receive
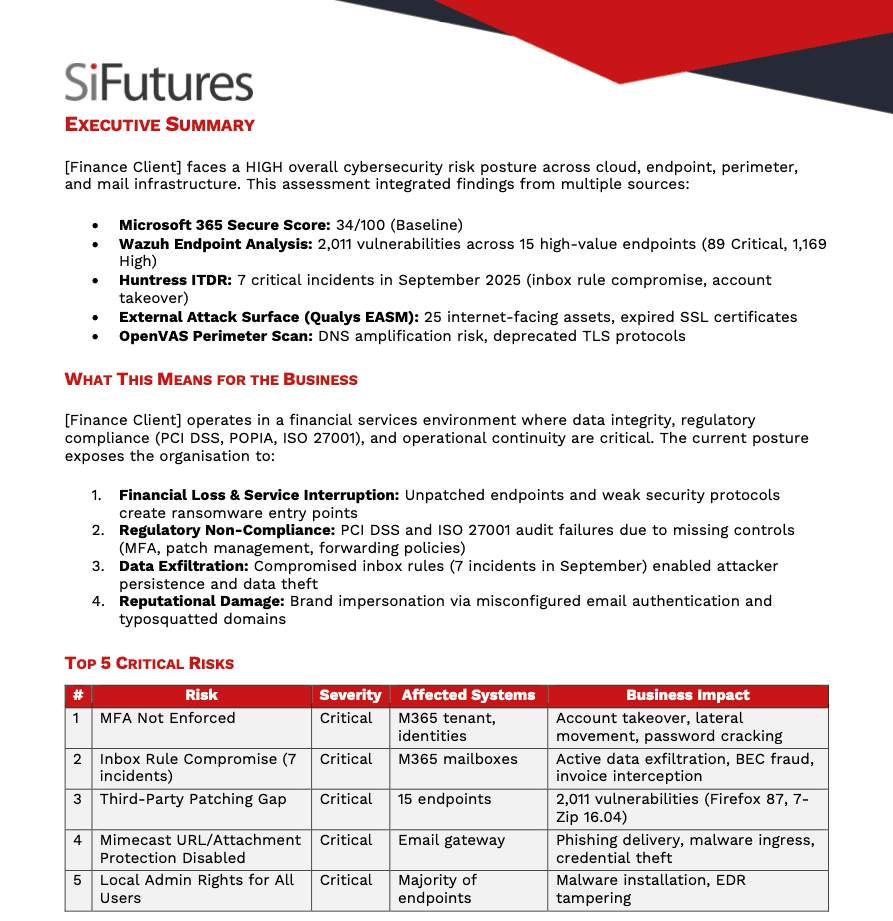
An executive summary that tells you the overall risk, what it could mean for the business and the five things to fix first. Behind it sits the detail your IT team or provider needs to do the work.
This example is from an assessment for a financial services client, anonymised.
Problems we've solved
A finance firm after an attempted invoice redirect
An attacker had tried to redirect an invoice payment. The assessment found a Microsoft 365 Secure Score of 34 out of 100, forwarding rules nobody had set up, email domains that could be spoofed, 25 systems visible from the internet and a lookalike domain already registered.
Within weeks, multi-factor authentication was enforced, link and attachment protection was switched on and the mail connector was locked down. Endpoint and identity protection came next.
Closing every door before someone else opens it
For a financial services company, lookalike domains were registered across every relevant extension, future registrations blocked and the brand watched every month. Read the story
Executive, aviation finance company
Related reading: Finding the vulnerability was never the hard part · What the handover document doesn't tell you · The MSP that decided to build its own operating system
Where the plan leads
Findings usually point to one of three places: Managed Firewall for the edge, Managed Detection and Response for devices and accounts, and Human Firewall for your people. You decide what to do next, and who does it.
Common questions
What is the difference between the free assessment and a full assessment?
The free Security Risk Assessment is a lighter version of SiSmic Surface: it looks at what anyone on the internet can see about your business, including your domains, email security and exposed systems. A full assessment adds your devices, network, Microsoft 365 configuration and logs, depending on the modules you choose.
We already have an IT provider. Can we still use this?
Yes. We share the findings and the plan with your existing provider so they can fix what we found. There is no obligation to move your support to us.
Will it disrupt our business?
No. Scanning is scheduled with you, and the plan balances security against how your people work, so fixes do not stop the business.
How is it priced?
Each module is a fixed scope at a fixed price, agreed before we start. Ongoing monthly monitoring of your internet-facing systems is optional.
Start with what anyone can already see
Our free Security Risk Assessment shows what your business looks like from the internet. Then we talk about what you actually need.
Get a free Security Risk Assessment